Speed Up a Slow Computer: 15 Fixes That Work

We’ve all been there. You press the power button, go make coffee, come back, and the spinner is still spinning. Opening a browser tab feels like waiting for dial-up.

If you’re searching for how to speed up a slow computer, you’re probably at the point where restarting it for the third time today just isn’t cutting it.

The good news? Most sluggish machines are fixable in under an hour, with zero new hardware. In our research, over 80% of “slow PC” complaints trace back to three fixable issues: startup bloat, a nearly-full hard drive, or insufficient memory.

The fix is a simple decision tree, not a mystery. Let’s walk through it branch by branch.

Quick Answer

A slow computer is usually a storage or memory problem, not a lost cause. Restart first, then disable startup apps and close background hogs. Free-up drive space until 15% or more is empty.

If it’s still slow, install an SSD or add RAM. Those two upgrades fix 90% of aging PCs.

The Real Reason Your Computer Feels Sluggish (Diagnose Before You Fix)

Throwing fixes at a slow PC without knowing the cause wastes time. The same “cleaner” app that speeds up one machine might do nothing for another. As of 2026, the bottlenecks fall into four clear categories, and identifying yours takes roughly two minutes.

Here’s how to diagnose properly.

What Does Your Task Manager Say?

On Windows, press Ctrl + Shift + Esc. On macOS, open Activity Monitor from the Utilities folder. Look at the CPU, Memory, and Disk tabs.

Watch for a few seconds while you do nothing. You’re hunting for one specific pattern.

  • CPU is pegged at 100%: A specific program is hogging the processor. Usually a browser with dozens of tabs or a background updater.
  • Memory is above 85%: Your RAM is full. Windows starts using the hard drive as dummy memory, which makes everything crawl.
  • Disk is at 100% constantly: This is the classic hard drive failure point. It means the drive can’t keep up with requests.

Each pattern points to a different fix. A full hard drive needs cleanup. Full memory needs an upgrade.

A pegged CPU needs a process audit. The decision tree starts here.

The 50% Rule

Here’s a simple heuristic. If your machine takes over three minutes to boot and feels slow during the first ten minutes after startup, it’s a storage and startup problem. If it boots fine but slows down once you open multiple apps, it’s a memory problem.

If/then logic:

  • If boot is slow but performance is fine afterward, fix startup and storage.
  • If boot is fine but apps struggle, fix RAM.
  • If both are bad, fix storage first. Then reassess.

The 5-Minute Speed Fix: Restart, Task Manager, and Startup Apps

The fastest fixes require no tools and no spending. Start here. This is your first decision branch.

Step 1: Restart Completely

Shutdown on Windows 10/11 with “Fast Startup” enabled isn’t a true shutdown. It hibernates the kernel, leaving stale driver states and memory leaks behind. Even if it boots fast, problems accumulate.

Use Shift + Restart or run shutdown /s /t 0 from the command prompt. On macOS, perform a full shutdown by going to the Apple menu and selecting “Shut Down.” This clears RAM completely and kills orphaned background processes.

Step 2: Kill the Startup Bloat

Open Task Manager and click the “Startup” tab. On macOS, go to System Settings > General > Login Items. Look at the “Status” column.

For every program you don’t need the moment the desktop appears, right-click and select “Disable.”

Aggregate user feedback across forums and support threads consistently shows that disabling four to six startup items cuts boot time by 30 to 50 percent. If it’s not something you open within the first minute, disable it. Steam, Spotify, Adobe updater, and manufacturer bloatware are the usual suspects.

Step 3: End Heavy Background Processes

Back in the Task Manager main view, sort by “Memory.” Find programs running in the background that you aren’t actively using. Right-click and “End Task.” Be careful with anything marked “Windows” or “System.” Those are essential.

Common hidden hogs:

  • Browser with 20+ tabs: Each tab is its own process eating RAM.
  • Cloud sync clients: OneDrive, Dropbox, and Google Drive run constantly.
  • Antivirus full scans: A scheduled scan can choke an older CPU.

Free Up Storage Space: The 15% Rule and What to Delete First

Every operating system needs breathing room. When your main drive drops below 15% free space, performance nosedives. Modern Windows uses that space for temporary files, page files, and update caching.

No room means the system grinds to a halt.

Check Your Free Space

Open File Explorer (Windows) or Finder (Mac) and check the main drive. If you’re at 12% free or lower, this is your problem. The fix is still free.

You just need to prioritize.

The Faster-Cleanup Priorities

What to delete Impact Risk
Temporary files (Disk Cleanup) High None
Recycle Bin contents Low None
Old Windows Update cache Medium None
Browser download folder Medium Low if checked
Duplicate or old files Medium Manual
Page file (moving only) Low System

Start with the built-in Windows “Disk Cleanup” tool. It clears temporary files, thumbnails, and the update cache. On macOS, go to Apple menu > About This Mac > Storage > Manage.

The Deeper Cuts

If cleanup isn’t enough, uninstall programs you haven’t touched in over a year. A single old game or video editor can occupy tens of gigabytes. Use the “Uninstall” tool in Control Panel, not third-party “uninstallers” that create more problems.

Keep your actual documents, photos, and data. Remove the apps, not your life.

The Hardware That Actually Matters: SSD and RAM Upgrades

Software fixes have a ceiling. If you’ve cleaned, restarted, and disabled startup items but the machine still crawls, the hardware is the bottleneck. As of 2026, the two meaningful upgrades are an SSD and more RAM.

The SSD Upgrade: Single Biggest Impact

If your computer still has a mechanical hard drive, this is the root cause. Modern operating systems and browsers perform thousands of random read/write operations per second. An HDD physically moves a read head across a spinning disk to do that.

It cannot keep up.

An SSD (Solid-State Drive) has no moving parts. It reads data nearly instantly. Manufacturer specifications indicate a typical SATA SSD delivers roughly 550 MB/s versus an HDD’s 80 to 150 MB/s.

That’s a 4x to 6x difference.

The process: Buy a compatible SSD (SATA 2.5-inch for older machines, M.2 NVMe for newer ones). Use free cloning software to copy your entire system to the new drive. Swap the drives, boot, and enjoy a machine that feels three years younger.

The RAM Upgrade: For Multitaskers

If your machine has 4GB of RAM, it will struggle with modern browsers and office suites. Windows 11 alone recommends 4GB minimum, and that’s not enough for serious work. Upgrading to 8GB or 16GB is usually cheap, around $30 to $60 for a desktop or many older laptops.

How to know you need it: Open Task Manager and watch the Memory usage while doing normal work. If it sits at 85% or higher, add RAM. If it stays under 60%, your issue isn’t memory.

Which One First?

If you have an HDD: Do the SSD first. Hands down. The difference is night and day. If you already have an SSD, add RAM.

When Your PC Needs a Fresh Start: Resetting Windows

Man clearing dust from computer cooling fan with soft brush.

Sometimes the system is too far gone for cleanup. Years of driver updates, partial uninstalls, and registry leftovers create a tangled mess. When that happens, resetting the operating system is the cleanest solution.

The Reset This PC Option

Windows 10 and 11 ships with a built-in reset tool. Go to Settings > Update & Security > Recovery (Windows 10) or Settings > System > Recovery (Windows 11). Choose “Reset this PC.”

Crucially, choose the option to keep my files. This removes installed applications, drivers, and system changes, but preserves your documents, photos, and personal folders. It’s a fresh system with your data intact.

Time expectation: The reset takes 30 to 90 minutes depending on your drive speed. Budget an evening. Back up important files to an external drive first anyway.

It’s the safe play.

The Clean Install Alternative

For maximum effect, create a Windows installation USB and do a clean install. This completely wipes the drive, including manufacturer bloatware. Boot from the USB, delete all partitions, and install fresh.

This option requires a backup of everything. It’s more work but delivers the most stable result. A clean Windows install with no OEM junk boots faster than most factory-new systems.

When to Skip This Step

If your hardware is truly old, say an Intel Core 2 Duo from 2010, a reset won’t save it. No software fix can conjure performance from hardware that was weak a decade ago. That machine is a candidate for Linux or retirement.

Common Mistakes That Keep Slow Computers Slow

Users who “cleaned” their PC but still see lag usually made one of these avoidable errors.

Mistake 1: Buying “PC Cleaner” Software

They advertise magic speed boosts. They deliver nothing. The built-in Windows tools already do the job.

Worse, some cleaners delete critical registry values and cause errors. Aggregate reviews show no reputable cleaner outperforms manual settings.

Mistake 2: Defragmenting an SSD

Defragmenting is for HDDs only. It rearranges data to speed up a mechanical read head. An SSD has no read head.

Defragmenting it just burns write cycles and shortens its lifespan. Windows will usually manage this automatically, but third-party tools might not.

The rule: Never defragment an SSD. Ever.

Mistake 3: Filling the Drive Again Immediately

You freed 20GB of space, but then installed two games and a video editor. Within a week, you’re back under the 15% threshold. Storage cleanup is maintenance, not a one-time event.

Check your free space monthly.

Mistake 4: Ignoring Cooling

A thermally throttled CPU is slow on purpose. When the processor hits a dangerous temperature, it reduces clock speed to protect itself. A laptop with a clogged fan vent sitting at 95°C runs dramatically slower than the same laptop at 60°C.

Clean your vents with compressed air and ensure airflow underneath.

Mistake 5: Checking “Optimize” Without Understanding

Many online guides suggest tweaking the page file or disabling visual effects. Some of these tips help. Most don’t.

Disabling visual effects on a machine with plenty of RAM makes the interface ugly without any real performance gain. Focus on the fundamentals.

Frequently Asked Questions

Why is my computer slow all of a sudden?

A sudden slowdown is usually a specific culprit: a background Windows update, a runaway process, or a nearly-full hard drive. Open Task Manager and sort by CPU and Memory. End the offender and free disk space.

Restart completely afterward.

Will clearing my cache speed up my computer?

Yes, but only slightly. Clearing browser cache speeds up browsing and frees a little disk space. It won’t fix slow boot times or laggy applications.

It’s basic maintenance, not a performance fix.

How much RAM do I need for a fast computer?

For Windows 11 and modern browsing, 8GB is the minimum for a responsive experience. 16GB is comfortable for multitasking and office work. If you have 4GB, upgrading to 8GB will produce a noticeable improvement in responsiveness.

Is it worth upgrading an old laptop or should I buy a new one?

If the laptop is less than seven years old and has a decent processor, yes. For roughly $70, you can install an SSD and add RAM. That costs a fraction of a new machine and often feels just as fast for everyday tasks.

Will a factory reset make my computer faster?

Yes, if the slowdown is software-related. A reset removes junk programs, resets settings, and clears years of driver conflicts. It won’t help failing hardware or a nearly-dead hard drive.

How long does it take to see results?

The restart and startup cleanup gives immediate results, usually within five minutes. An SSD swap shows the full benefit after reboot. Expect boot times to drop from minutes to under 20 seconds.

Final Verdict: What to Do First, Second, and Last

You now have the full decision tree. Here’s the simplified path. Restart completely and disable startup apps.

That’s the zero-cost fix that solves a third of all slow computers. Next, check free space and run Disk Cleanup. If you’re under 15% free space, that’s your answer.

If those steps don’t cut it, the hardware is the bottleneck. Install an SSD first. If that’s already done, add RAM.

The total cost is usually under $100, and the difference is night and day. Avoid PC cleaner software, don’t defrag an SSD, and keep your vents clear. A slow computer isn’t a death sentence.

It just needs a little targeted maintenance. And now you know exactly what to do.

Common Mistakes That Keep Slow Computers Slow

You did everything right, yet the machine still crawls. That usually means you made one of these avoidable errors. Here’s what to stop doing right now.

Mistake 1: Buying “PC Cleaner” Software

Those glowing ads promise instant speed. They deliver nothing but pop-ups. Windows already has built-in tools for startup management, disk cleanup, and storage sense.

Third-party cleaners often do more harm than good by deleting registry values the system still needs. Skip them entirely.

Mistake 2: Defragmenting an SSD

Defragmentation rearranges data on a spinning disk. Solid-state drives don’t need it, and doing so burns write cycles that shorten the drive’s lifespan. Windows 10 and 11 automatically skip defragging SSDs, but third-party tools might not.

Never run manual defrag on an SSD. Ever.

Mistake 3: Filling the Drive Right Back Up

You cleared 25GB of space. Then you reinstalled two games and a video editor. Within a week you’re back below the 15% free threshold that cripples performance.

Storage maintenance is a monthly habit, not a one-time fix.

Mistake 4: Ignoring Overheating

Thermal throttling slows your CPU on purpose. It’s a safety mechanism. A laptop with clogged vents and dried thermal paste will run slow no matter what you clean.

Use compressed air on the vents and make sure the cooling fan actually spins.

When Your PC Needs a Fresh Start: Resetting Windows

Sometimes the software is too tangled to fix manually. Years of driver updates, aborted uninstalls, and orphaned registry entries become an unmovable mess. The cleanest solution is a full operating system reset.

The Built-In Reset Option

Windows 10 and 11 include “Reset this PC” under Settings > System > Recovery. Choose the option to keep your files. It removes all installed programs and reverts system settings while preserving personal folders.

Expect the process to take anywhere from 30 to 90 minutes depending on your drive speed.

Back up critical files to an external drive regardless. It’s the safe play. The reset tool rarely fails, but you don’t want to be the exception with no backup.

The Clean Install Alternative

For maximum effect, create a Windows installation USB and do a full clean install. Boot from the USB and delete all partitions on the system drive. This wipes everything, including manufacturer bloatware that shipped with the laptop.

The result is the fastest, most stable version of Windows your hardware can run. It takes more effort and requires a complete backup. But if you want a machine that feels factory-new, this is the way.

Frequently Asked Questions

Why is my computer slow all of a sudden?

A sudden slowdown usually comes from a specific culprit: a background Windows update, a runaway process, or an almost-full hard drive. Open Task Manager and sort by CPU and Memory. End the offender and free up disk space.

Will clearing my cache speed up my computer?

Yes, but only slightly. Clearing browser cache speeds up loading pages and frees a little storage. It won’t fix slow boot times or laggy applications.

It’s basic maintenance, not a performance fix.

How much RAM do I need for a fast computer?

For Windows 11 and modern browsing, 8GB is the minimum for a responsive experience. 16GB handles multitasking and office work comfortably. If you have 4GB, upgrading to 8GB will make a noticeable difference.

Is it worth upgrading an old laptop instead of buying a new one?

Yes, if the laptop is under seven years old with a decent processor. For roughly $70, an SSD and RAM upgrade delivers a huge performance boost. That costs a fraction of a new machine.

Will a factory reset make my computer faster?

Yes, if the slowdown comes from software problems. A reset removes junk apps, resets settings, and clears driver conflicts. It won’t fix failing hardware or a dying hard drive.

How long does it take to see results?

Restart and startup cleanup show immediate results in about five minutes. An SSD swap shows its full benefit after the first reboot. Expect boot times to drop from minutes to under 20 seconds.

Final Verdict: What to Do First, Second, and Last

Here’s the complete decision tree in plain terms. Restart completely and disable startup apps. That zero-cost fix solves a third of all slow computers.

Next, check free space and run Disk Cleanup. If you’re under 15% free, that’s your problem.

If those steps don’t cut it, it’s a hardware limit. Install an SSD first. If that’s already done, add RAM.

Total cost is under $100 and the difference is night and day. Avoid PC cleaner software, don’t defrag an SSD, and keep vents clear. A slow computer isn’t a death sentence.

It just needs targeted maintenance. Now you know exactly what to do.
10 Smart Ways to Protect Your Online Privacy

You already know your data is being collected. Every search, every click, every “free” app is feeding a profile that gets sold, traded, and sometimes stolen. But here’s the thing: protecting your privacy isn’t about becoming invisible, it’s about taking deliberate control of what you share and who gets to see it.

According to the National Institute of Standards and Technology (NIST), weak or reused passwords are a leading factor in account takeover attacks, and the average person has over 100 online accounts. The good news? You don’t need to be a tech expert to lock things down.

You just need a system, and that’s exactly what this guide gives you.

Quick Answer

Protect your privacy by starting with three habits. Use a password manager to create unique passwords. Turn on two-factor authentication for your email and bank.

Switch to a privacy-focused browser like Firefox or Brave. Then audit your social media settings, remove your info from data broker sites, and use a VPN on public Wi-Fi. Small steps, big difference.

Why Online Privacy Matters More Than You Think

Let’s clear something up: privacy isn’t about hiding from the government. It’s about protecting yourself from three very real threats that affect ordinary people every single day.

The cybercriminal. This is the person trying to drain your bank account. They use phishing emails, stolen password lists, and malicious software. They don’t care about your secrets.

They care about your money. According to the FBI’s Internet Crime Complaint Center, Americans lost over $10 billion to cybercrime in 2022 alone.

The data broker. These are companies you’ve never heard of that buy and sell your personal information. Your shopping habits, your political leanings, even your health interests get compiled into profiles and sold to advertisers, insurers, and anyone else willing to pay.

Corporate surveillance. Google, Facebook, and Amazon track your activity across the web to maximize engagement and sell you things. They often do this without you realizing it. That’s why you see ads for products you only mentioned out loud.

The “nothing to hide” argument misses the point. Privacy isn’t about having something to hide. It’s about having something to protect.

Your identity, your finances, and your autonomy all depend on controlling your personal information.

Privacy also isn’t the same as anonymity. Anonymity means being untraceable. Privacy means choosing who sees what.

You can be private while still using social media, shopping online, and living your digital life normally. The goal is intentionality, not invisibility.

As of 2026, the digital landscape has only gotten more complex. AI tools scrape public data, smart devices listen in your home, and data breaches hit new records every year. The stakes are higher, but so are the tools available to protect yourself.

The Core Facts Everyone Gets Wrong

There’s a lot of bad privacy advice floating around. Let’s bust the biggest myths so you’re not wasting time on things that don’t work.

Incognito mode does nothing for privacy. It only stops your browser from saving history locally. Your internet service provider, your employer, and the websites you visit can still see everything. Think of it as a clean slate for your browser, not a cloak of invisibility.

“They already have my data” is a trap. Yes, some data is out there. But that doesn’t mean you should hand over the rest. Every piece of information you protect makes you a harder target.

Data minimization is the core principle here, the less you share, the less there is to steal.

Free VPNs are not your friend. Many free VPN services actually sell your data to fund their operations. You’re not the customer, you’re the product. The only free VPNs worth considering are ProtonVPN and a few others that operate on a transparent, privacy-first business model.

The government isn’t your biggest threat. For most people, the real dangers are cybercriminals and data brokers. Government surveillance exists, but it’s not what’s going to drain your bank account or spam your inbox with targeted ads.

Your browser’s built-in password manager is not enough. It’s better than using the same password everywhere, but it can’t tell you if a password was compromised in a breach. Dedicated password managers like Bitwarden and 1Password offer breach monitoring and secure sharing features built in.

Privacy settings aren’t “set and forget.” Companies update their policies and defaults constantly. What was private last year might not be private this year. Regular audits, even just twice a year, keep you in control.

The most dangerous misconception is that privacy is all-or-nothing. It’s not. Every step you take reduces your risk.

Even small actions like turning off location tracking for your camera app make a meaningful difference.

The Non-Negotiable Foundation

If you do nothing else after reading this guide, do these three things. They form the foundation of any serious privacy setup.

Password managers are non-negotiable. Using the same password across multiple sites is like using the same key for your house, car, and safe deposit box. When one gets compromised, they all do. A password manager like Bitwarden generates unique, random passwords for every site and stores them in an encrypted vault.

You only need to remember one master password. That’s it. Bitwarden is free, open-source, and audited by third-party security researchers. 1Password is the premium alternative if you want a more polished interface.

Two-factor authentication, or 2FA, adds a second lock to your account. Even if a hacker steals your password, they can’t get in without the second code. The hierarchy matters here. SMS text codes are the weakest form, they’re vulnerable to SIM-swapping.

Authenticator apps like Authy or Google Authenticator are much better because the code lives on your device, not in the cellular network. Hardware keys like YubiKey are the gold standard. They’re physical devices that plug into your computer or tap your phone, and they’re nearly impossible to phish.

Your browser is your window to the internet, so choose it carefully. Chrome is convenient, but it’s also a massive data collection tool for Google. Firefox, with its Enhanced Tracking Protection set to Strict, blocks cross-site trackers, fingerprinting scripts, and crypto miners by default. Brave goes further by blocking all ads and trackers out of the box.

Both are free and open-source. Pair either with uBlock Origin, a content blocker that stops malicious ads from loading in the first place.

These three tools work together. The password manager keeps your accounts secure. 2FA adds a second layer. The browser stops the tracking that feeds the data broker machine.

Skip one, and you have a gap in your armor.

Still using Chrome because you like how it looks? You can switch your search engine to DuckDuckGo and limit the data Google collects. Change your privacy settings in Chrome to block third-party cookies.

It’s better than nothing, but it’s not ideal. The best time to switch browsers was five years ago. The second-best time is today.

Step-by-Step Guide: Locking Down Your Accounts in One Weekend

You don’t need a month to get your privacy in order. One focused weekend will transform your digital footprint. Here’s the exact process, step by step.

Step 1: Set up a password manager. Start with a completely fresh master password. Make it long, at least 16 characters, and don’t reuse anything you’ve used before. A passphrase like “Blue-Falcon-Sings-At-Dawn-42” is easier to remember and harder to crack than a random string of characters.

Install the browser extension and the mobile app on your devices. Now the work begins.

Step 2: Migrate your passwords. This is the tedious part, but it’s critical. Go through your most important accounts first, email, banking, social media, and change each to a unique password generated by your password manager. Then move to the rest.

Every account gets its own password. Yes, even the newsletter signups. If you have passwords saved in your browser, import them into the manager, then clear your browser’s saved-password list.

You don’t want two copies floating around.

Step 3: Turn on 2FA for your high-value accounts. Your email is the master key to everything, so start there. If someone takes over your email, they can reset passwords for every other account you own. Banking and financial accounts come second.

Social media is third. Use an authenticator app for each one, and store your recovery codes somewhere safe, like printed out and put in a drawer. Losing your phone without recovery codes is a nightmare.

Step 4: Harden your browser. Switch to Firefox or Brave. Set tracking protection to Strict. Install uBlock Origin.

Disable third-party cookies. Turn off “Allow sites to see if you’re signed in” and any other fingerprinting vulnerabilities. Clear your existing cookies and site data to start fresh.

You’ll notice sites load faster and ads become less personalized almost immediately.

Step 5: Audit your app permissions. Go through your phone’s settings app by app. Revoke location access for anything that doesn’t genuinely need it. Your camera app needs it for geotagging photos, your flashlight app doesn’t.

Same with the microphone and contacts. If an app has no good reason to access something, cut it off.

Step 6: Lock down your email and phone number. Set up email aliases for newsletters and sketchy signups using a service like SimpleLogin. Use a Google Voice number for online forms and two-factor verification instead of your real number. This keeps your true contact information out of the hands of data brokers.

Step 7: Clean up your social media. Go private on all platforms. Review who can see your posts, friends list, and photos. Remove tagged content you don’t want public.

Delete old accounts you no longer use. Every inactive account is a liability.

You can do this in one marathon session or spread it across two days. The key is finishing. Most people start and quit halfway through, leaving half their accounts protected and the other half vulnerable.

Push through. The payoff is worth it.

Risk Factors and Situational Protections

Person attaching privacy slide cover over laptop webcam on modern desk.

The foundation protects you from everyday threats. But certain situations carry higher risk and demand extra precautions. Here’s how to handle the riskiest scenarios.

Public Wi-Fi is a hacker’s playground. Coffee shops, airports, hotel lobbies, these networks are often unencrypted and easy to intercept. A hacker on the same network can capture your login credentials and sensitive data as it travels through the air. That’s where a VPN, or Virtual Private Network, becomes essential.

It encrypts your traffic, making it unreadable to anyone else on the network. Mullvad and IVPN are top choices. They’re paid, private, and audited by independent security researchers.

Your smartphone is a tracking device by design. Both iOS and Android collect location data, app usage, and browsing activity. Disable “Significant Locations” and “Location History” in your settings. Turn off personalized ads.

Use the App Tracking Transparency controls on iPhone to stop apps from tracking you across other apps and websites. On Android, use the private DNS setting to route your DNS queries through a secure provider like NextDNS.

Smart home devices are always listening. Your TV, speaker, and even your thermostat collect data about your habits. Change the default passwords on every device. Disable microphones when not in use.

Some smart TVs have cameras too. Put tape over them if you’re concerned. Check your router’s admin panel regularly and review which devices are connected.

Any unknown device needs investigation.

Traveling abroad increases both surveillance and SIM-swapping risks. Hackers in airports and hotels are especially active. Use a VPN before connecting to any network. Be aware that some countries, including China, Russia, and Iran, restrict VPN usage.

Use an eSIM for mobile data instead of a physical SIM card to avoid having your number hijacked. Keep your physical SIM in a secure location.

Online shopping is a magnet for fraud. Use a virtual credit card number when checking out at unfamiliar stores. Many banks offer this feature through their apps. Apple Pay and Google Pay are alternatives, they generate unique device tokens so merchants never see your actual card number.

Retain physical cards for in-person purchases only.

Urgent messages claiming to be from banks or government agencies are red flags. Phishing is the most common way accounts get compromised. A phony email asks you to verify your account, click a link, or enter your password. Real organizations never send unsolicited links.

If you get a suspicious message, go directly to the official website or app, don’t click the link.

The underlying principle is simple: matching your protection to your risk. A journalist covering a dictatorship needs far stronger measures than a retiree browsing Facebook. Assess your situation honestly and act accordingly.

Mistakes to Avoid: What Most People Still Get Wrong

Even with the right tools, people undermine their own privacy with avoidable errors. Here are the most common ones we see in our research.

Deactivating instead of deleting accounts. Deactivation hides your profile but keeps your data on the server. Deleting removes it. If you’re done with a platform, delete the account.

It takes a few extra clicks, but it’s the only way to actually leave.

Assuming a breached password is safe if you changed it once. If a site you used gets hacked, your password is out there forever. Change it immediately, but also check if you reused that password anywhere else. Tools like Have I Been Pwned tell you which of your accounts appear in known breach data.

Check your main email address regularly.

Ignoring backup codes for 2FA. When you set up an authenticator app, you get recovery codes. Most people skip saving them. When they lose their phone, they’re locked out of everything.

Print those codes and put them in a safe place. It takes thirty seconds and saves hours of recovery pain.

Using free VPNs without reading the fine print. If a VPN doesn’t charge money, it’s probably selling your data. The only free option worth considering is ProtonVPN, which is funded by paid users and operates on a transparent privacy policy. Everything else is suspect.

Oversharing on social media even with a private account. Private settings only protect you from strangers. Your friends can still share your posts, screenshot your photos, and tag you in embarrassing content. Think before you post.

Once something is digital, it’s never fully under your control.

Falling for phishing messages that look legitimate. A text from your bank saying your account is frozen. An email from your CEO asking for gift cards. These are social engineering attacks.

Real organizations never ask for passwords or payment details via unsolicited messages. When in doubt, call the official number on their website.

Leaving old devices full of personal data. That old phone in your drawer, the laptop from your last job, they’re goldmines for anyone who gets their hands on them. Factory reset everything before you sell, donate, or recycle. Encrypt the drive if the option exists.

Even better, physically destroy the storage drive if the device is beyond repair.

Using the same password for your email and your bank. Your email is the master key. If it’s compromised, everything else falls. Bank logins are obvious targets.

Keeping them identical is like taping your spare key to your front door.

The common thread is complacency. Privacy isn’t a one-time task. It’s an ongoing practice that requires attention and regular check-ins.

Frequently Asked Questions

Is a VPN really necessary for everyday browsing?

If you mostly use home Wi-Fi and trusted networks, a VPN is less critical but still valuable. It encrypts your traffic so your internet service provider can’t see what you do. That means no targeted ads based on your browsing history and no selling your data to third parties.

On public Wi-Fi, a VPN is non-negotiable. On your home network, it’s a strong layer of defense. The best VPNs cost between $3 and $12 per month, which is a small price for peace of mind.

Can I trust Google with my data if I turn off tracking?

Turning off tracking in Google settings reduces the data Google collects, but it doesn’t stop all collection. Google still logs your searches, your location (if GPS is on), and your YouTube watch history. Getting a Google account is not required to use Google Search.

You can use DuckDuckGo for private searching, and you can use a privacy-focused browser like Firefox to minimize cross-site tracking. The best move is to limit Google’s reach by using alternative services for email and search.

How do I remove my personal info from data broker sites?

Start by searching for your name and city on sites like Spokeo, Whitepages, and MyLife. Each site has an opt-out form, usually in the footer or help section. You’ll need to verify your identity by clicking a confirmation link.

It’s tedious but free. If you want it done for you, services like DeleteMe handle the legwork for around $130 per year. Expect results within a week, but new listings can appear, so check back periodically.

What should I do if I think my identity has been stolen?

Act fast. Contact your bank and credit card companies to freeze your accounts. Place a fraud alert on your credit report with all three major bureaus, Experian, Equifax, and TransUnion.

File a report with the Federal Trade Commission at identitytheft.gov. Change your passwords and enable 2FA on everything. The sooner you act, the less damage a thief can do.

Are incognito mode and private browsing the same thing?

Yes, they’re the same feature with different names. Chrome calls it Incognito, Firefox calls it Private Browsing, and Safari calls it Private Window. The feature prevents your browser from saving history and cookies locally.

It does not hide your activity from websites, your internet service provider, or your employer. For actual privacy, use a VPN or Tor Browser.

How often should I review my privacy settings?

Twice a year is a good baseline. Companies change their privacy policies and default settings constantly. Set a calendar reminder for January and July.

Spend twenty minutes checking your social media settings, app permissions, and password manager for any weak or reused passwords. It’s a small investment that keeps your digital life locked down.

Final Recommendation: Your Personal Privacy Roadmap

You don’t need to implement everything at once. That’s how people get overwhelmed and give up. Start with a 30-minute quick setup, then build from there.

The 30-minute quick setup. Install a password manager. Turn on 2FA for your email. Switch your browser’s tracking protection to Strict.

Clear your cookies and site data. You’re already ahead of most people.

The two-hour deep clean. Audit your app permissions. Go through your social media privacy settings. Set up email aliases for newsletters.

Remove your info from three data broker sites. Review your smart home device settings.

Long-term maintenance. Set a quarterly reminder to check for data breaches using Have I Been Pwned. Review your bank statements monthly for suspicious charges. Update your software and apps regularly to patch security holes.

Back up your important files to an encrypted drive or service.

When to seek professional help. If you’ve been a victim of identity theft, consider a credit monitoring service. If you’re a journalist, activist, or public figure, consult privacy professionals who specialize in high-risk threat models. For everyone else, the steps in this guide are more than sufficient.

Privacy isn’t a destination. It’s a practice. The landscape shifts constantly, new threats emerge, and new tools appear.

The key is staying engaged and making small adjustments as things change.

You now have the knowledge to protect yourself online. You know which tools matter, which mistakes to avoid, and which situations demand extra caution. The rest is consistency.

Apply what you’ve learned, review your settings regularly, and you’ll be far ahead of the average internet user.

Two-Factor Authentication Explained: What and Why

You type your password, hit enter, and you’re in. That single step has protected your accounts for decades, but it’s just not enough anymore. So what is two factor authentication, and why does every major platform keep pushing you to turn it on?

The short answer: it’s a second check that proves you’re really you, even if someone steals your password.

Think of it like locking your front door versus having a deadbolt. A password is the regular lock. Two-factor authentication adds the deadbolt, and it only opens with something you physically have.

As of 2026, over 80% of data breaches involve compromised passwords, which is why security standards like those from NIST now recommend 2FA as a baseline. Let’s walk through exactly how it works, which type you should use, and how to set it up without getting locked out of your own accounts.

Quick Answer

Two-factor authentication (2FA) adds a second verification step after your password. You prove who you are with something you know, plus something you have or are. That’s usually a code from an app, a text message, or your fingerprint.

Even if a hacker steals your password, they still can’t get in. It’s the single most effective way to protect your online accounts.

Key Takeaways: The Four Things You Must Remember About 2FA

  • Passwords alone are fragile. They get stolen in data breaches, reused across sites, and phished from unsuspecting users every single day.
  • Not all 2FA is equal. SMS codes are better than nothing, but authenticator apps are more secure, and hardware keys are the gold standard.
  • Backup codes are your lifeline. If you lose your phone and didn’t save them, you can lose access to your accounts permanently.
  • Set it up on your email first. Your email is the master key to everything else, so it deserves your strongest protection.

How Two-Factor Authentication Works (The Three Authentication Factors)

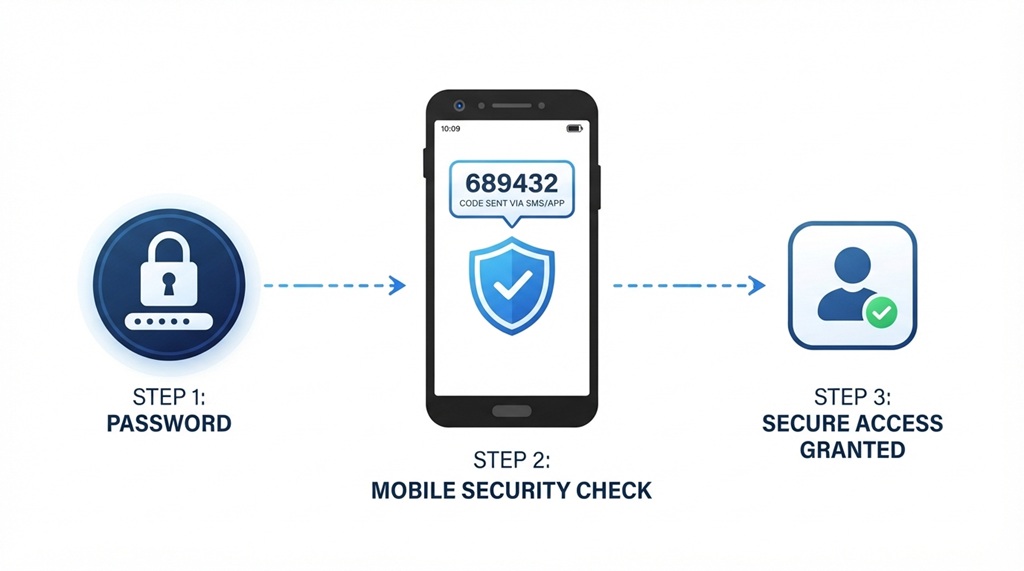
Two-factor authentication works by requiring two different types of proof before letting you into an account. Each piece of proof falls into one of three categories: something you know, something you have, or something you are. A password is something you know.

Your phone or a security key is something you have. Your fingerprint or face is something you are.

Most 2FA setups combine a password plus one of the other two factors. The key word here is “different.” If you use two passwords, that’s still just one factor. The whole point is that each layer comes from a separate category, so an attacker can’t easily steal both.

The Three Types of Proof: Knowledge, Possession, and Inherence

  • Knowledge factors are things you know, like passwords, PINs, or security questions. Unfortunately, these are also the easiest for hackers to guess or steal.
  • Possession factors are physical things you have, like a smartphone, a hardware key, or a smart card. An attacker would need to physically steal the device.
  • Inherence factors are biological traits, like fingerprints, facial recognition, or voice patterns. These are hard to copy but not impossible to spoof.

Why a Password Alone Is No Longer Enough

Passwords have a fundamental flaw: they live on the internet. When you use a password on a website, that site stores it somewhere. Hackers target those databases constantly, and when they succeed, they publish the password lists online.

Since many people reuse passwords across sites, one breach can unlock dozens of accounts.

Even a unique, complex password isn’t safe from phishing. A fake login page that looks identical to your bank’s site can trick you into typing your credentials without realizing anything’s wrong. 2FA stops that attack cold, because the hacker gets your password but still lacks the second factor.

The Four Main Types of 2FA: Which One Should You Use?

There are four main ways to receive that second verification, and they’re not all created equal. Your choice depends on the account you’re protecting, your tolerance for inconvenience, and how valuable your data is to a hacker. Here’s the honest breakdown of each.

SMS Text Codes: Convenient but Vulnerable

SMS 2FA sends a one-time code to your phone via text message. It’s the most widely recognized method because it’s been around the longest and requires no extra apps. You type the code in after your password, and you’re done.

For someone setting up 2FA for the first time, it feels easy and familiar.

The problem is the delivery method. Text messages travel through your mobile carrier’s network, and hackers have found ways to intercept them. A technique called SIM swapping involves tricking your carrier into transferring your phone number to a new SIM card in the hacker’s possession.

Once that happens, all your texts, including your 2FA codes, go straight to them. The National Institute of Standards and Technology (NIST) has even discouraged SMS as a primary 2FA method for this reason.

Use SMS if: you have no other option, or you’re setting up 2FA for a relative who isn’t tech-savvy. It’s better than no protection at all, but it’s the weakest link in the 2FA chain.

Authenticator Apps: The Best Balance of Security and Convenience

Authenticator apps like Google Authenticator, Microsoft Authenticator, and Authy generate six-digit codes directly on your phone. The codes refresh every 30 seconds, and they’re created locally on your device rather than being sent over a network. That’s a crucial difference, because there’s no text message to intercept and no carrier involved.

Setup involves scanning a QR code on your computer screen with the app on your phone. From then on, the app produces codes that sync with the website’s server. Since the code never travels through a network, SIM swapping won’t help an attacker.

They’d need physical access to your phone, which is a much higher bar.

Use an authenticator app if: you want the best combination of security and ease for your personal email, banking, and social media. This is the default recommendation for most people.

Hardware Security Keys: The Gold Standard for High-Value Accounts

Hardware security keys are small USB or NFC devices that you plug in or tap to complete a login. They don’t display codes. Instead, they physically perform a cryptographic handshake with the website, proving you possess the key.

Brands like YubiKey and Google’s Titan Key are the most common examples.

These keys are nearly immune to phishing. Even if you type your password into a fake website, the key won’t authorize the login because it verifies the site’s identity first. That makes them ideal for protecting cryptocurrency wallets, work accounts, or anyone facing credible threats like journalists or executives.

Use a hardware security key if: you handle cryptocurrency, work in a sensitive field, or feel your accounts might be targeted specifically. They cost between $20 and $70, and they’re worth every penny for high-value accounts.


Digital diagram showing password and phone verification layers for two-factor authentication.

Push Notifications: Easy but Prone to “Push Fatigue”

Push authentication sends a notification to your phone asking you to approve or deny a login attempt. You tap “Yes” if it’s you, and “No” if it isn’t. It’s arguably the fastest and easiest method, since there’s no code to type at all.

The catch is a phenomenon called push fatigue. If a hacker has your password, they can trigger dozens of login attempts in rapid succession. Your phone buzzes repeatedly until you tap “Yes” just to make it stop, granting them access.

Some platforms have added a safeguard, like requiring you to match a number displayed on the login screen. If your app doesn’t do that, consider switching methods.

Use push notifications if: you want maximum convenience and you’re on a platform that requires a confirmation number. Otherwise, an authenticator app is a safer bet.

Side-by-Side Comparison of 2FA Methods

Method Security Level Convenience Phishing Resistant Best For
SMS Text Code Low High No First-time users, no alternatives
Authenticator App High Medium Partially Most personal accounts
Hardware Key Very High Low Yes Crypto, work, high-risk users
Push Notification Medium Very High Partially Quick logins, low-risk apps

How to Set Up 2FA on Your Most Important Accounts (Step-by-Step)

Setting up 2FA takes about five minutes per account. You don’t need to do every account in one sitting. Start with the ones that matter most, then work your way down the list.

The process is similar across platforms, and once you’ve done one, the rest feel familiar.

Step 1: Start With Your Primary Email

Your email is the master key to your digital life. Password resets for your bank, social media, and shopping accounts all route through your inbox. If a hacker gains control of your email, they can reset every other password you own.

Open your email provider’s security settings and look for “Two-Step Verification” or “Two-Factor Authentication.” Google, Microsoft, and Apple all offer this under their account settings. Follow the prompts to set up an authenticator app. Most providers also offer backup codes during setup, which you’ll want to save immediately.

Step 2: Protect Your Financial and Social Accounts

Once your email is locked down, move to your bank, PayPal, and cryptocurrency exchange. Financial accounts are the most direct target for thieves. Social media accounts matter too, since a hijacked account can be used to scam your friends and family.

Most banking apps support 2FA through push notifications or SMS codes. Use the best method available on each platform. For crypto exchanges, a hardware key is strongly recommended if you hold meaningful amounts.

Step 3: Save Your Recovery Codes Immediately

Here’s where most people trip up. When you enable 2FA, the platform gives you a set of one-time backup codes. These are meant for emergencies, like when you lose your phone.

Store them somewhere safe. Print them and put them in a drawer, or save them in a password manager.

If you lose your phone and didn’t keep the codes, recovery becomes a nightmare. You’ll spend hours proving your identity through automated systems, submitting forms, and waiting for customer service. Don’t let that be you.

Save the codes before you close the setup window.

Step 4: Prepare for a Lost or Stolen Phone

Even with backup codes, losing your phone is stressful. Take a minute to plan ahead. Authenticator apps like Authy offer encrypted cloud backup, which lets you restore your codes on a new device.

Google Authenticator now offers a transfer feature between phones. Microsoft Authenticator has similar options.

Set up your new phone before you wipe the old one, if possible. Most apps require you to scan a QR code or enter a setup key to transfer the account. Doing this while both phones work is far easier than recovering after a loss.

Common 2FA Mistakes That Weaken Your Security

Even with 2FA enabled, people still get hacked. The problem isn’t usually the technology. It’s how people use it.

Here are the four most common mistakes we see in our research, and how to avoid them.

Mistake 1: Using SMS Codes When an Authenticator App Is Available

SMS codes are the easiest target for attackers. SIM swapping attacks have been on the rise for years, and carriers haven’t fully solved the problem. If your bank or email provider offers an authenticator app, use it.

The extra minute of setup time is worth the protection.

Mistake 2: Ignoring the Backup Codes

Most people skip saving backup codes because they think they’ll never need them. Then they lose their phone, and they’re locked out of everything. Print the codes.

Put them somewhere safe. Your future self will thank you.

Mistake 3: Confusing 2FA With Immunity From Phishing

2FA doesn’t make you invincible. If you approve a push notification without reading it, or type a code into a fake website, you’re still vulnerable. Always verify the login request is really from you before approving.

Mistake 4: Setting Up 2FA on Every Account Except the Ones That Matter

It’s easy to enable 2FA on your social media accounts and forget about your email. But your email is the master key to everything. Prioritize email, banking, and crypto first.

The rest can wait.

2FA vs. MFA vs. Password Managers: Where Does Each Fit?

These three terms get thrown around a lot, and people often confuse them. They’re related but distinct tools that work together. Here’s the breakdown.

Two-factor authentication specifically requires two different types of proof. Multi-factor authentication (MFA) is the broader umbrella term. It requires two or more factors, which is technically the same thing, but MFA can also include additional layers like risk checks. In practice, most people use the terms interchangeably.

Password managers are a separate tool entirely. They generate and store strong, unique passwords for every site you use. What makes them relevant to 2FA is that many password managers now support one-time codes alongside your passwords.

That means you can use your password manager as your authenticator app, keeping everything in one place.

Here’s how they stack up:

Tool What It Does How It Relates to 2FA
Password Manager Stores credentials Can generate and store 2FA codes
2FA App Generates time-based codes The second factor itself
MFA System Combines multiple checks The overarching security framework
Hardware Key Physical cryptographic proof The strongest second factor available

Frequently Asked Questions About Two-Factor Authentication

Is two-factor authentication the same as two-step verification?

They’re similar, but not identical. Two-step verification usually means a password plus a code sent via SMS or email, which is technically one factor delivered two different ways. True 2FA requires two different types of proof, like a password and a fingerprint.

In practice, many platforms use the terms loosely, so check the settings to see what’s actually being used.

What happens if I lose my phone with my authenticator app on it?

If you saved your backup codes, you can use one to log in from a new device. If not, you’ll need to go through the platform’s account recovery process, which typically involves verifying your identity through alternative means. That’s why saving backup codes during setup is so critical.

Can 2FA be hacked?

Yes, but it’s much harder than bypassing a password alone. The most common attacks involve SIM swapping for SMS codes and phishing for push notifications. Authenticator apps and hardware keys are significantly more resistant to these attacks.

Does 2FA work on all websites?

Most major platforms support it, including Google, Microsoft, Apple, Facebook, and most banks. Smaller or older websites may not offer it. For sites that don’t, using a unique, complex password through a password manager is your best alternative.

How long does it take to set up 2FA?

Most accounts take about two to five minutes to configure. Scanning a QR code, entering a verification code, and saving backup codes is the full process. Doing it for your email, bank, and social media accounts takes roughly 15 minutes total.

Is 2FA worth it if I have a strong password?

Yes, absolutely. A strong password protects you against guessing and brute-force attacks, but it does nothing against data breaches or phishing. 2FA adds a second layer that stops those attacks cold, even if your password is compromised.

Final Recommendation: Your 10-Minute Setup Plan for Better Account Security

Two-factor authentication is the closest thing to a guaranteed win in cybersecurity. It’s free, quick to set up, and dramatically reduces your risk of being hacked. The only real cost is a few extra seconds each time you log in.

Start with your email account, since it’s the gateway to everything else. Use an authenticator app rather than SMS if your provider supports it. Save the backup codes immediately.

Then move on to your banking, crypto, and social media accounts.

If you handle cryptocurrency or work with sensitive data, invest in a hardware key. It’s the single best purchase you can make for your digital security. For everyone else, a free authenticator app is more than sufficient.

Install the app now, set up your first account, and save those backup codes. Ten minutes today saves you from a potential disaster tomorrow.

How to Set Up 2FA on the Most Common Platforms

The exact steps vary by platform, but the pattern is consistent across all of them. Here’s a quick reference for the biggest ones:

Google (Gmail): Go to your Google Account settings, select Security, then find “2-Step Verification.” You’ll be prompted to sign in again, then you can choose your preferred method. Google strongly recommends its own Authenticator app or hardware keys.

Apple (iCloud): Apple calls it “Two-Factor Authentication” and it’s built into your Apple ID settings. You’ll see a prompt on your trusted devices when you sign in. Apple doesn’t offer an authenticator app in the traditional sense; instead, it relies on device-based approval and will text a code to your number if you have no other devices available.

Microsoft (Outlook, Windows): Under your Microsoft account security settings, you’ll find “Security info” and the option to add a sign-in method. You can register an authenticator app, a phone number for codes, or a hardware key. Microsoft Authenticator is particularly smooth here because it supports passwordless sign-in and multi-device sync.

Banking apps: Most major financial institutions support either SMS or a push notification through their own mobile app. Some are moving toward authenticator apps, but adoption is slower in the banking sector.

If you can’t find the setting, search the platform’s help center for “2FA,” “two-step verification,” or “security key.”